The GRC platform with the method built in
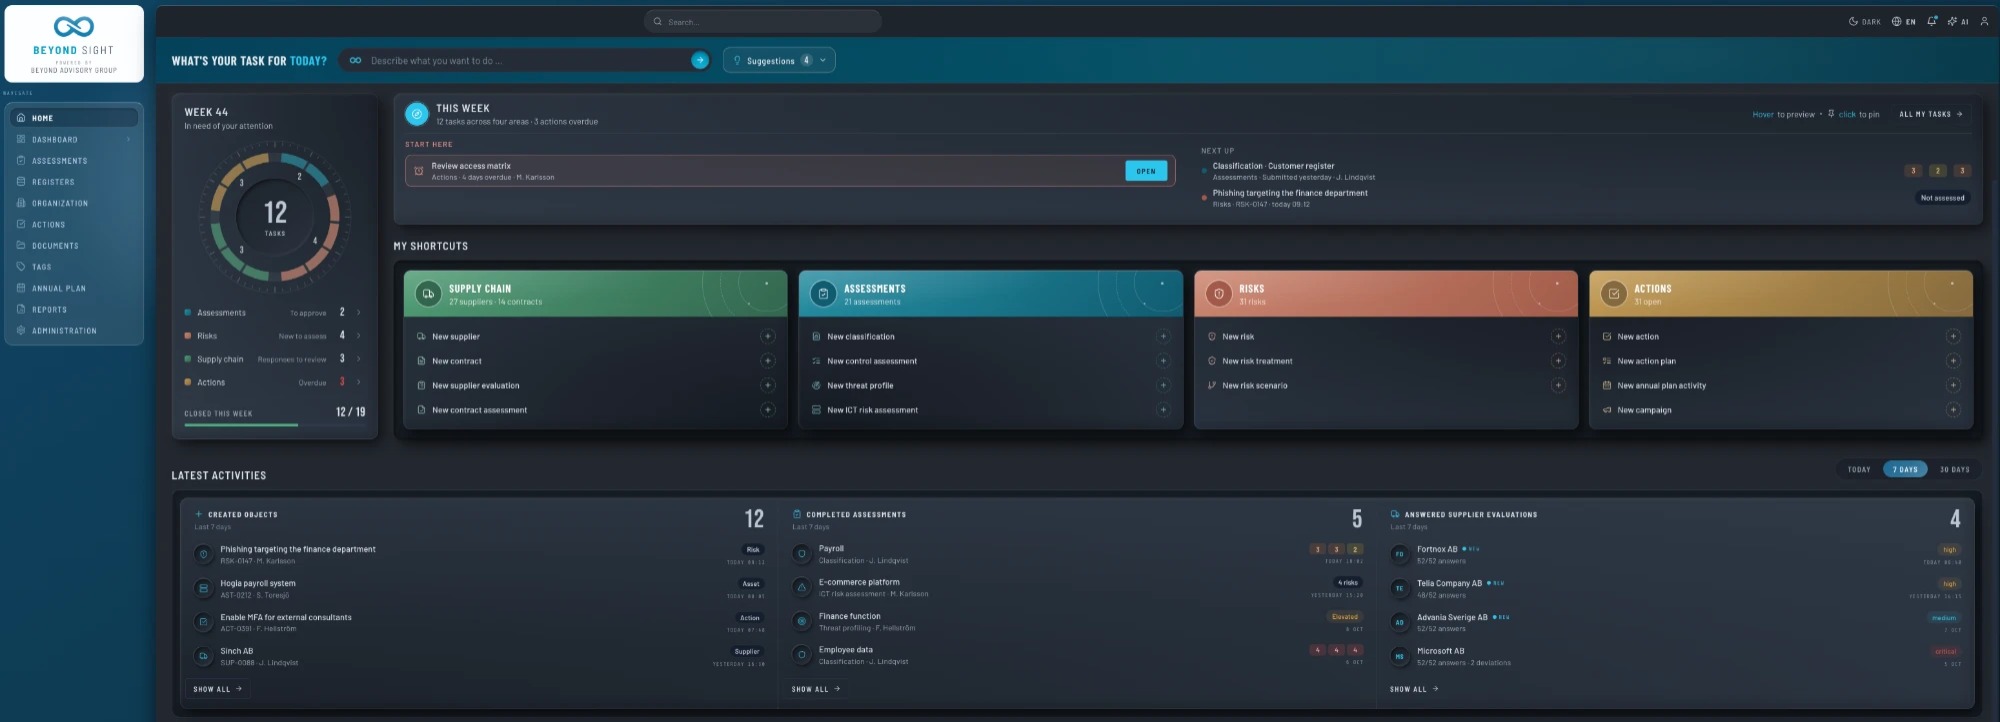
BeyondSight brings your compliance, risk and supplier work into one connected platform. Our methodology guides each step, guided AI helps with the heavy lifting, and every decision stays on the record.
One way of working, from start to follow-up
BeyondSight takes you from identifying what you have to approving and following up, with the same steps every time. Predictable for your team, traceable for anyone who checks it later.
Classify
Map information assets and systems and classify them by confidentiality, integrity and availability.
Profile
Identify the threats that matter to your organisation. The threat profile steers what to assess first.
Assess
Structured assessments of risks, suppliers and contracts, linked to your classifications and threats.
Manage
One register with owners, actions and review dates, and a plan for the year's work.
Follow up
Track actions and review dates, and give management a clear picture with the record behind it.
One connected register
Everything lives in one register, where risks, controls, suppliers and systems are linked to each other.
Compliance
Frameworks, requirements, controls and scope, linked across frameworks.
Suppliers and contracts
Registers by criticality, critical ICT suppliers flagged, questionnaires via secure link and recurring contract reviews.
Risks and threats
Threat profiling, step-by-step vulnerability assessments and one risk register with owners and review dates.
Information and systems
Classification and a system overview, with approval.
Follow-up
Actions, an annual plan and an overview of where things stand.
Five steps, every time
Create, assess, review, publish, follow up. Approvals update the audit log automatically.
AI that helps. You decide.
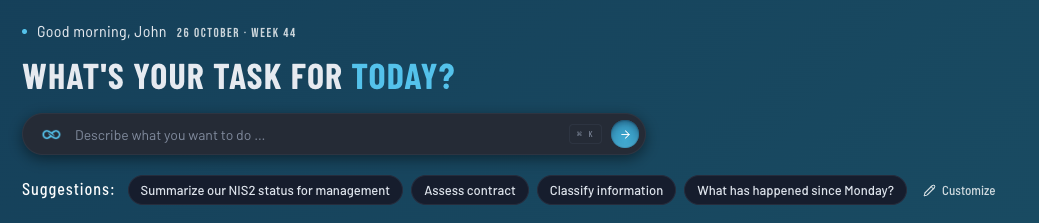
We use AI where it saves you effort, not where it would take your judgement. It helps with drafting, structuring and finding the right information, so your team can spend more of its time on the decisions.
- Gives expert suggestions to weigh up, grounded in our methodology, for example threats that may be relevant to a system.
- Helps you draft and summarise, from your own data in the platform.
- Answers questions about where things stand.
- Never approves on your behalf. Approvals are made by people, and they're logged.
When someone asks why
Every approval, scope decision and change is logged, with who did it and when. Assessments are kept as they were when you approved them. Risks have owners and review dates. So when the board, an auditor or the supervisor asks why, the answer is already there.
Bring us a real question
Book a demo and bring something real from your compliance work. We'll show you how BeyondSight handles it.